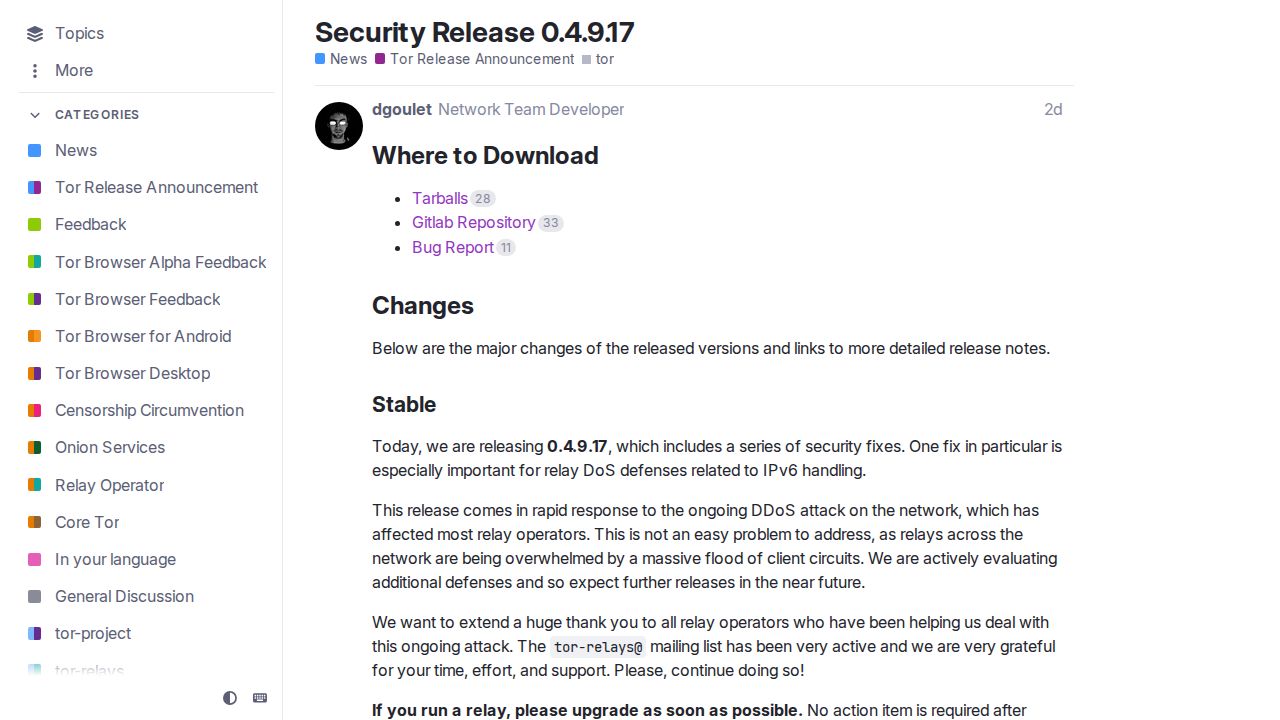
Relay operators on the Tor network have reported extreme performance degradation, with some users experiencing download speeds dropping by as much as 99% during a sustained system-wide DDoS attack. In response, the Tor Project issued a rapid-response security release (0.4.9.17) specifically designed to defend against this ongoing threat.
The Tor Project's Rapid Response
The Tor Project has issued a security release, version 0.4.9.17, to address a sustained Distributed Denial of Service (DDoS) attack. This rapid-response fix aims to stabilize the network against the influx of malicious traffic.
The primary goal of the update is to provide immediate defense mechanisms for relays, which are the servers that facilitate the anonymous routing of data across the Tor network.
Impact on Relay Operators
Relay operators have reported severe consequences from the attack, including nodes being marked as 'overloaded' in relay searches. One operator reported that their download speeds dropped by 99% from normal levels until the relay was turned off.
The scale of the disruption suggests a system-wide impact rather than a localized issue. This degradation affects the reliability of the network for both the operators hosting the infrastructure and the users relying on it.
Community Discussion and Analysis
Commenters on Hacker News discussed the potential motivations and mechanics behind the attack. One commenter suggested that while DDoS attacks are often directed at specific competitors, this event appears to be system-wide, potentially affecting relays caught in the middle of a specific attack.
Others argued that the attack might be the work of a state actor or a targeted strike where every node not compromised by the actor is treated as a single target. There was also discussion regarding whether the attack is bypassing Tor's existing Proof of Work (PoW) challenges.
A technical limitation noted by a commenter was the occurrence of 403 errors when trying to access Tor's own website through the network, though other users reported the site remained accessible through different configurations.
Unresolved Questions
The specific identity of the attacker and the exact technical nature of the DDoS—whether it is volumetric or protocol-specific—remain unconfirmed in the provided reports.
The situation is described by some as a 'cat and mouse game,' where the project must continually adapt its defenses as attackers find new ways to overwhelm the network's infrastructure.
pull_quote
I noticed the attack when my mom said the wi-fi wasn't working well and I checked it out and the download speed was down 99% from normal.
source_id": "50513763" (hn-50512441) -- Note: The prompt requires the quote to be from the source text. Since this is a discussion digest, the quote is from the comment.