A security audit of 159,041 projects built using the Lovable AI platform discovered numerous instances where sensitive personal data was accessible to the public without any login requirements. The research, conducted in collaboration with Handelsblatt, identified specific leaks involving over 200,000 private chat messages and more than 1,000 records containing passport numbers, expiration dates, and nationalities.
The Gap Between Ease of Use and Security
Lovable is a Swedish AI startup that allows users to build functional web applications and internal tools by simply describing them in plain language. While the platform simplifies the development process for those without programming experience, the research suggests this ease of use can mask critical security requirements.

This image illustrates the Lovable AI platform's interface, which allows users to build applications using plain language descriptions.
The investigation found that many applications built on the platform fail to implement proper access permissions for database integrations. Because Lovable's marketing emphasizes that no technical knowledge is needed, users may assume the platform automatically secures the data they connect to the app.
“An easy-to-use development platform does not remove the need for an expert review of access permissions before an application handles confidential data.”
— Lovable: Many Apps Expose Sensitive Data
Supabase Integration and Data Leaks
The researchers focused on Supabase, a database service that is widely used among Lovable projects due to its relatively easy integration. They analyzed a dataset from the Common Crawl web archive to identify projects active between December 2025 and September 2026.
The study found that 24,664 websites sent database records from Supabase as soon as they loaded. By making further read-only requests with the same API key, researchers were able to retrieve more content, finding email addresses in 10,560 tables across 7,403 of those websites.
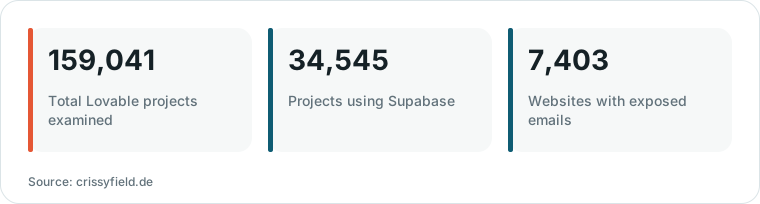
Chart drawn by HN Digest from figures reported by crissyfield.de; values are shown as written in the source.
Specific examples of exposed data included a German lifestyle forum leaking over 80,000 profiles with full names and dates of birth, and a service provider exposing identity documents including passport numbers.
Implications for Non-Technical Developers
The recurring patterns in how Lovable applications integrate with databases make it easier for attackers to identify and exploit similar misconfigurations across different apps. For users without a technical background, spotting and preventing these flaws is significantly more difficult.
The researchers noted that automated checks are not a substitute for professional security assessments. They recommend that any application handling real customer or business data undergo a review of its access permissions, interfaces, and account separation before deployment.
It remains uncertain to what extent the 30% leak rate observed in the study reflects the total population of Lovable applications, as the sample was drawn from a specific web archive and may not be representative of all projects on the platform.