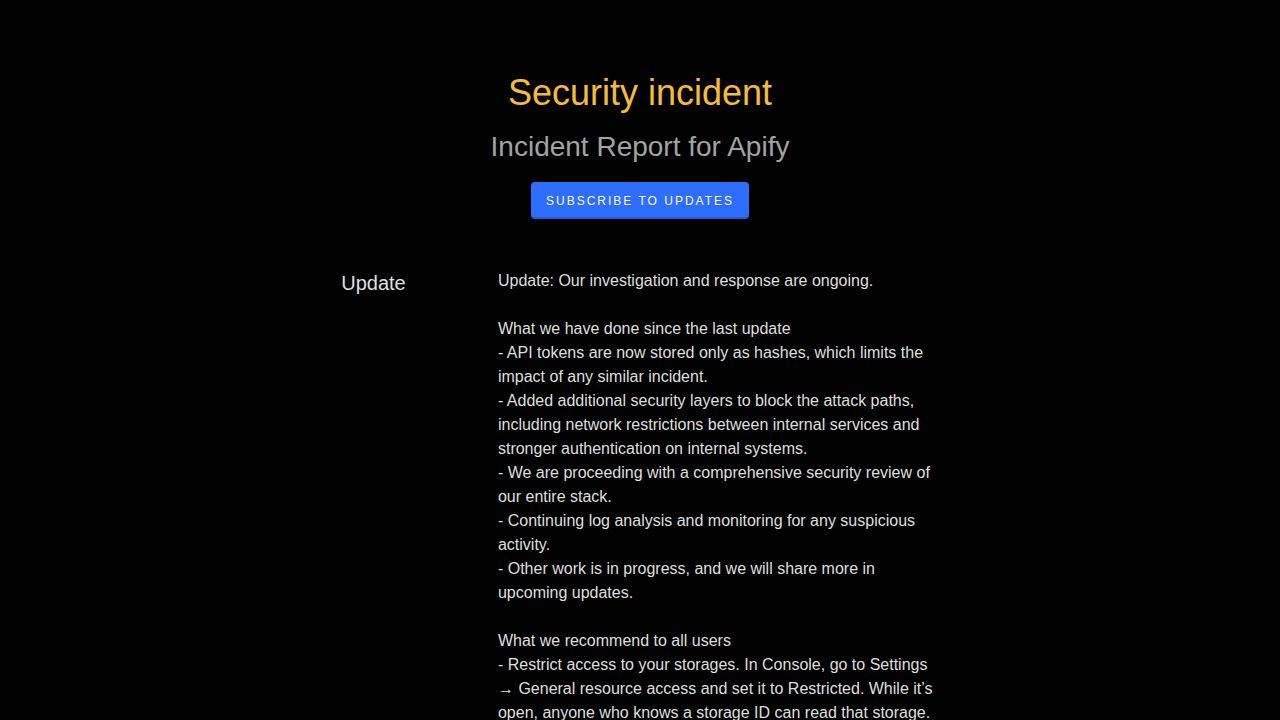
Apify detected an unauthorized third party using a compromised credential to access its internal systems and a number of account credentials between November 9 and 10, 2026. The breach was identified on November 11, at which point the company cut off the attacker's access and initiated a comprehensive investigation into the scope of the data accessed.
Detection and Immediate Response
Apify identified the unauthorized activity on November 11 at 12:13 UTC. Following detection, the company revoked several OAuth connections to external integrations, including GitHub, as a precautionary measure.
While the investigation did not find that these revoked connections were used as an attack vector, the company rotated various critical internal secrets and added additional monitoring to its systems.
“API tokens are now stored only as hashes, which limits the impact of any similar incident.”
— Security incident
Infrastructure Hardening and Mitigation
To mitigate the risk of future incidents, Apify updated its architecture so that API tokens are now stored only as hashes. This change is intended to limit the impact of any similar credential-based attacks.
The company also implemented new security layers, including network restrictions between internal services and stronger authentication protocols for internal systems. A comprehensive security review of the entire stack is currently underway.
User Actions and Data Privacy
Apify recommends that users restrict access to their storages by navigating to Settings and setting 'General resource access' to 'Restricted.' Without this setting, anyone who knows a storage ID can read that storage.
Users who build Actors from private GitHub repositories are instructed to reconnect their GitHub accounts by selecting 'Change provider' within the Actor settings. Apify has stated that it will not contact users who have not yet been identified as affected by the breach.
Remaining Uncertainties
The specific root cause of the initial credential compromise remains under investigation. Apify has committed to publishing a post-mortem report detailing the root cause and remediation steps within one week of the incident.
What Hacker News readers are saying
- Alternative: One commenter suggested that Bleeping Computer's coverage provided more specific details regarding Apify's response, such as the rotation of API tokens and 2FA resets. comment ↗
- Skeptical: A commenter expressed skepticism regarding the company's security practices, questioning why API tokens were not already stored as hashes. comment ↗
- Open question: Another user pointed out a perceived lack of transparency from the company regarding the specific types of data included in the leak. comment ↗
Summarized opinions from the Hacker News thread, not verified facts. Read the full discussion ↗