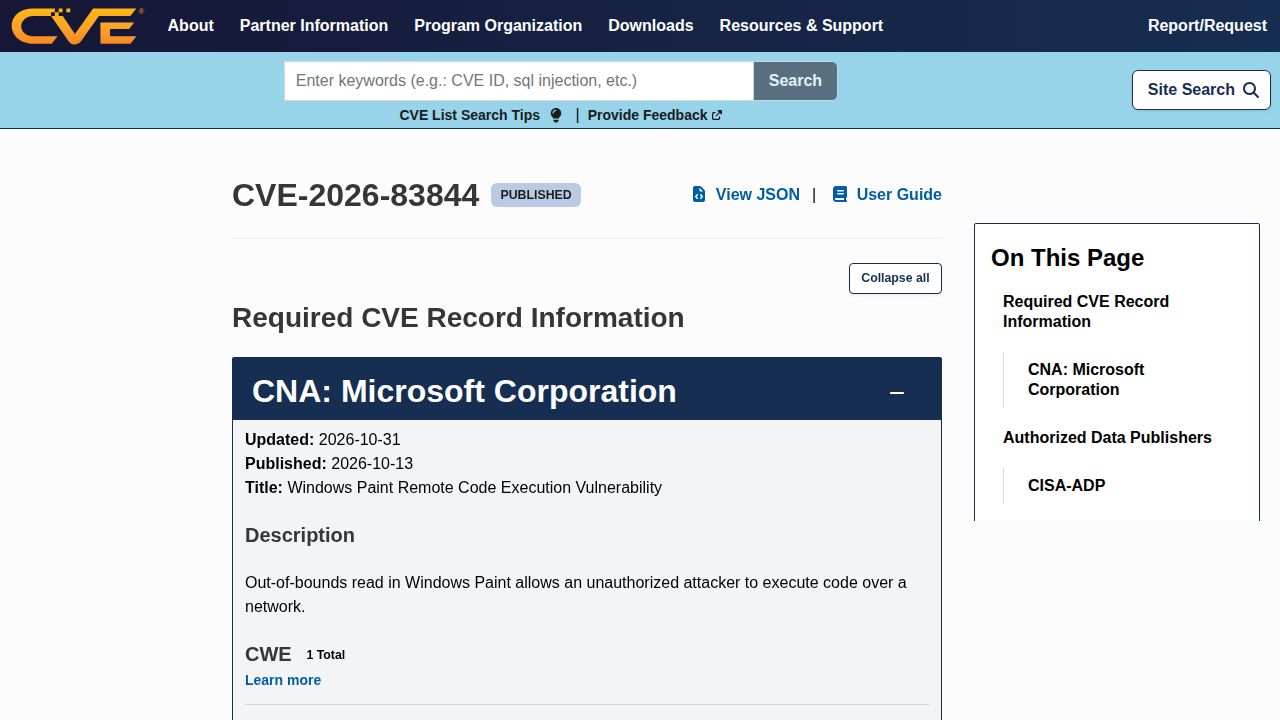
The modern iteration of the MS Paint application, which differs significantly from the classic 'mspaint.exe' utility, has been linked to a remote code execution (RCE) vulnerability (CVE-2026-83844). Unlike the legacy version, the current 'Paint' app includes advanced features such as layers and background removal, which has led to its evolution into a more complex software component. The vulnerability specifically affects versions ranging from 11.0.0.0 up to, but not including, 11.2605.91.0.
According to the CVE disclosure, an unauthenticated attacker could exploit this flaw by sending a specially crafted packet to an affected service over the network. This description implies that the application—or a service associated with it—is reachable over a network, a characteristic that has caused significant skepticism among users. Some observers noted that the vulnerability appears to require no user interaction and no authentication, leading to questions about whether the 'remote' nature of the bug is a result of the app's modern architecture or a potential boilerplate reporting error in the CVE documentation.
Remediation for the flaw involves updating the application to a patched version. Some users reported that the fix did not appear automatically through standard Windows Update, requiring a manual update via the Microsoft Store. While the specific mechanism of how a paint application exposes a network-accessible service remains unclear from the provided data, the vulnerability highlights the security implications of modernizing legacy desktop tools with networked capabilities.