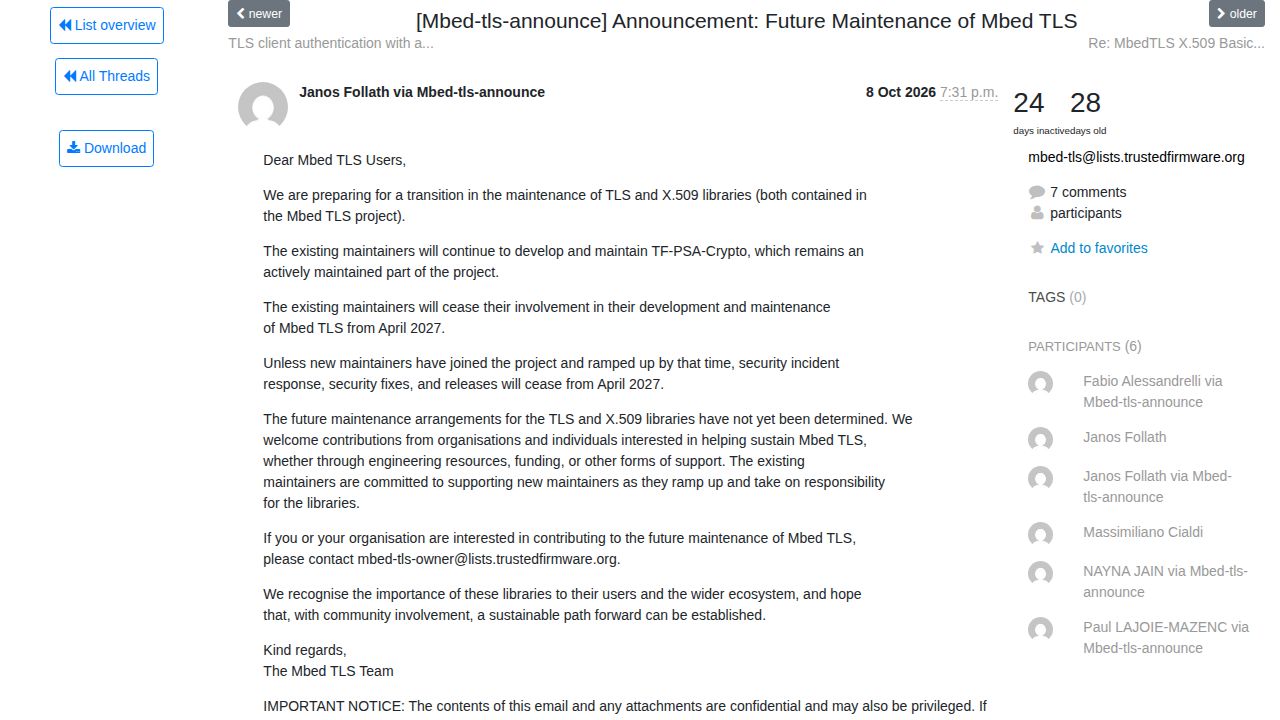
The Mbed TLS project, a widely used suite of cryptographic libraries, is entering a significant maintenance transition. The current maintainers have announced that they will officially cease their involvement in the development and maintenance of the core TLS and X.509 libraries starting in April 2027. While the team will continue to support the TF-PSA-Crypto component of the project, the core libraries—which provide the foundational security protocols for many embedded systems—face a potential gap in support unless new maintainers are recruited and onboarded before the deadline.
This transition poses a risk to the project's ability to provide critical security incident responses, security fixes, and regular releases. The Mbed TLS team has issued a call for organizations and individuals to contribute engineering resources, funding, or other forms of support to establish a sustainable path forward. The current maintainers have committed to assisting new maintainers during a transition period to help them ramp up and take over responsibility for the libraries. However, as of the announcement, the specific future maintenance arrangements for these libraries remain undetermined.
For users of the library, particularly those integrated into large ecosystems like Zephyr, this news highlights the challenges of sustaining community-driven open-source projects. The announcement follows a history of long-standing feature requests—such as support for PKCS#7 authenticated attributes—that have remained unaddressed for years. Without a confirmed successor or a new maintenance organization, users of Mbed TLS may find themselves relying on a library that lacks a clear path for security updates after April 2027. The project's future now depends on the community's ability to mobilize and provide the necessary resources to fill the void left by the departing maintainers.