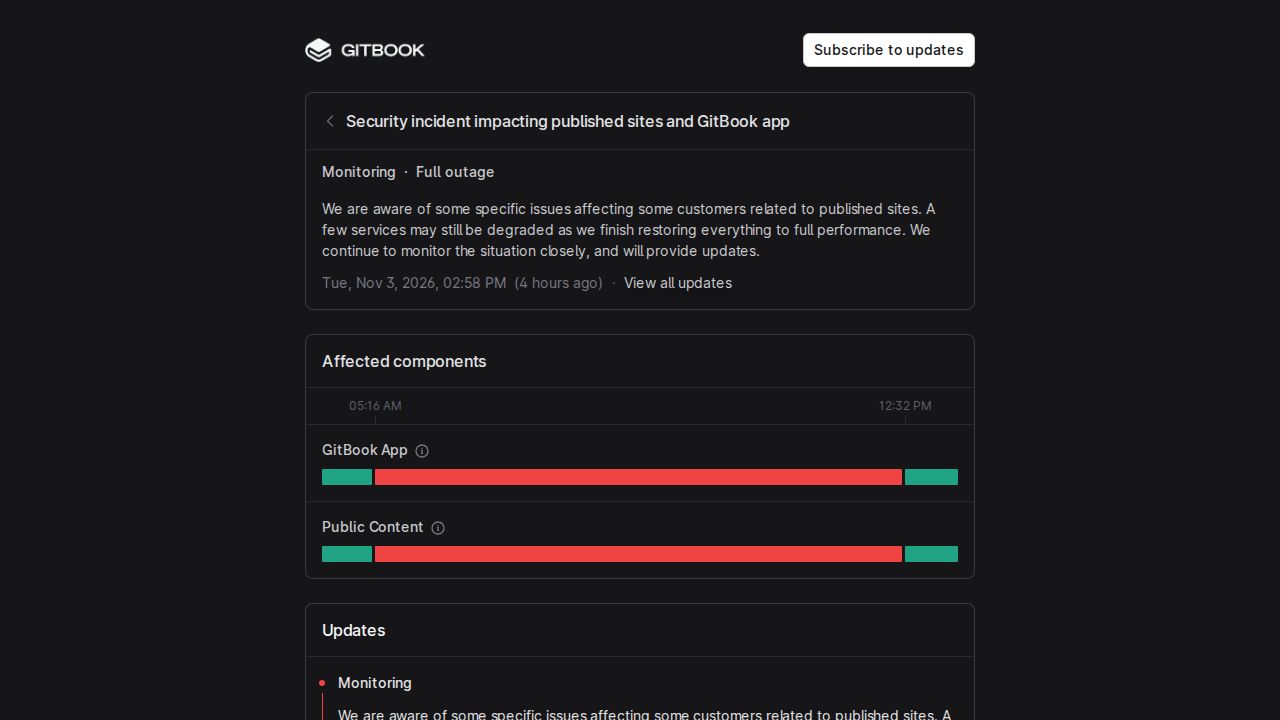
GitBook, a platform used for hosting and managing documentation, experienced a sophisticated security breach beginning on November 2, 2024. According to a disclosure from the company, the incident involved a highly targeted attack utilizing AI agents to gain unauthorized access to certain infrastructure credentials. In response to the detection, GitBook took the app and authenticated documentation sites offline to block the attacker and secure the environment. The company has since replaced all infrastructure secrets and is progressively restoring services to full performance.
The investigation into the breach suggests that several types of sensitive data may have been accessed by the attacker. These include Git Sync secrets, GitBook API tokens, and third-party API tokens used to connect external tools to the platform. Additionally, the company noted that questions asked by site visitors to the GitBook Assistant may have been accessed. While GitBook stated they found no evidence that any actual content within the documentation was modified, the exposure of these authentication tokens poses a significant risk to the integrations and automated workflows tied to the platform.
To mitigate the impact, GitBook has invalidated all customer API tokens and advises all users to take immediate action. Users are instructed to rotate any existing GitBook API tokens, as well as any third-party API tokens or secrets used to connect external tools. Furthermore, those with published integrations using secrets or those using the GitBook MCP server are required to rotate those secrets and re-authenticate their servers. While the company is preparing a full post-mortem, some users have noted discrepancies between the information provided on the official security incident page and the company's status page, and have expressed a desire for more specific technical details regarding how the infrastructure credentials were initially compromised.