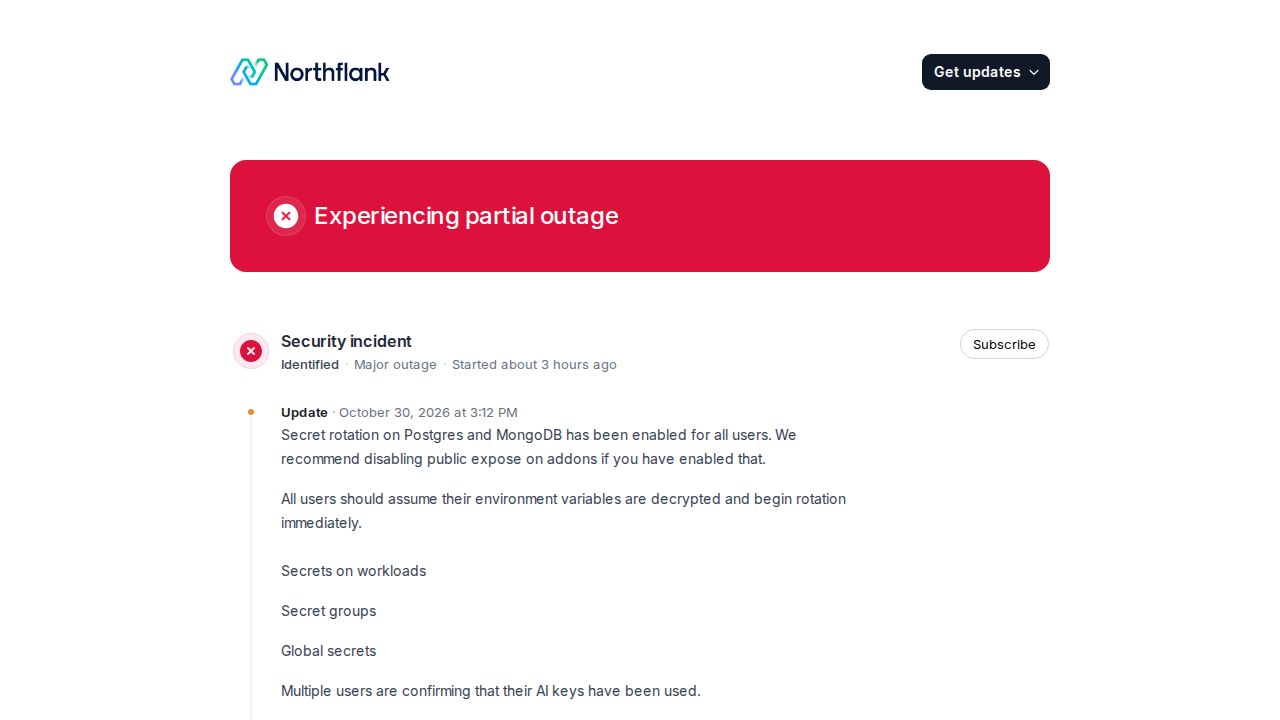
Northflank, a Platform-as-a-Service (PaaS) provider that simplifies application deployment, recently reported a security breach. The incident has prompted a broader discussion regarding the security posture of modern PaaS offerings, often referred to as 'neoclouds.' These platforms aim to provide a more user-friendly experience than traditional cloud infrastructure, but the breach highlights the risks associated with outsourcing core infrastructure management to third-party startups.
Commenters on Hacker News discussed the structural challenges of securing a PaaS environment. One commenter, writing as btown, pointed out a fundamental architectural difficulty: because users and automated agents expect to view environment variables (such as API keys and secrets) directly through a management UI or Command Line Interface (CLI), these credentials cannot be easily segregated from the public-facing web environment. While encryption at rest is a standard defense, the requirement to display these values means that a compromise of the management or API web server could allow an attacker to obtain secrets through impersonation.
The breach also fueled a debate over whether users should migrate back to established hyperscalers. One commenter, dangoodmanUT, suggested that the 'nicer to use' experience of infrastructure startups may not be enough to outweigh security requirements, particularly for enterprise customers. Others questioned the actual security superiority of hyperscalers, while some argued that advancements in AI are making self-hosting easier by lowering the technical barrier to managing Linux systems. Despite these differing views, the incident underscores the tension between the ease of use provided by modern PaaS and the rigorous security demands of production environments.