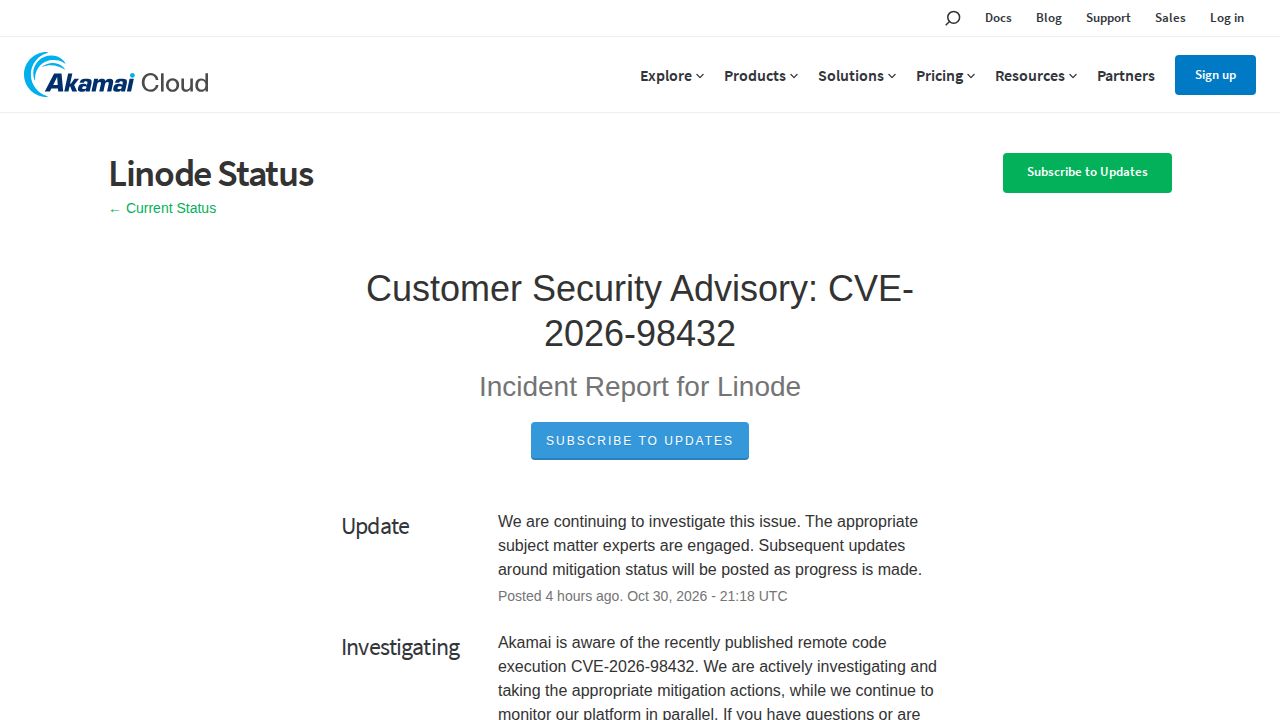
Linode, a cloud infrastructure provider, has officially reported a security incident via its status page. While the specific technical details of the breach remain limited in the initial report, the announcement has prompted significant scrutiny regarding the nature of the event and the current state of infrastructure security. Some observers noted that the lack of specific details might suggest the company is currently in the process of patching a newly identified vulnerability rather than responding to a confirmed, large-scale data exfiltration.
In the accompanying discussion, commenters expressed concern over a perceived 'inflection point' in cybersecurity, where the frequency of reported hacks is beginning to overwhelm the news cycle. A recurring theme in the conversation is the role of artificial intelligence in modern threats. Some participants suggested that AI-powered attacks are transitioning from targeting high-liquidity assets like cryptocurrency to targeting broader infrastructure and Software as a Service (SaaS) platforms. These commenters argued that the next phase of this trend could see a surge in attacks against traditional infrastructure, banks, and small businesses, potentially necessitating a shift toward 'defensive AI' to counter automated, high-speed threats.
Despite the alarm, other perspectives in the thread emphasized that standard security best practices—such as using secret managers, encryption, robust firewall rules, and backups—remain effective for most users who are not high-value targets. One commenter argued that the perceived 'security armageddon' may be exacerbated by users offloading critical security thinking to LLMs, which can lead to skipped steps in the security lifecycle. The discussion highlights a tension between the fear of automated, high-frequency AI attacks and the continued relevance of fundamental security hygiene for the average service provider.