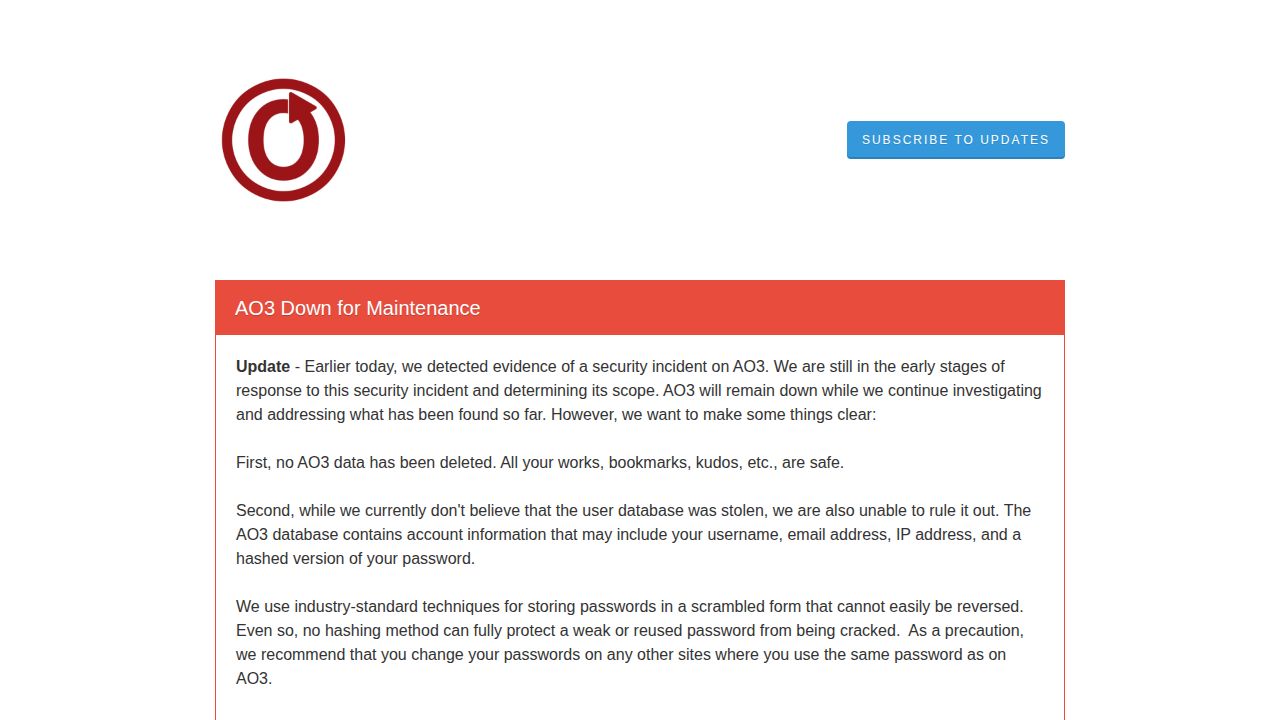
Archive of Our Own (AO3), a popular platform for hosting fanfiction and original works, has suspended its services for maintenance following the detection of a security incident. According to a statement from the platform's administrator, the site remains offline while the team investigates the scope of the breach and addresses identified vulnerabilities. The administrator clarified that no user-generated content, such as stories, bookmarks, or 'kudos' (a form of social appreciation), has been deleted or compromised during the event.
The primary concern involves the potential exposure of the user database. While the administrator stated they do not currently believe the database was stolen, they noted they cannot rule out such a possibility. The database contains sensitive account information, including usernames, email addresses, IP addresses, and hashed versions of user passwords. The platform uses industry-standard hashing techniques to scramble passwords, but the administrator cautioned that these methods cannot fully protect weak or reused passwords from being cracked if the data is accessed by unauthorized parties.
In the accompanying discussion, users highlighted the potential social and privacy consequences of such a leak, comparing the risk of exposing personal interests and reading habits to other high-profile data breaches. Some participants suggested that moving toward more robust authentication methods, such as WebAuthn (which allows the use of physical security keys), could mitigate the risks associated with password hashes. However, others noted practical limitations to such a transition, pointing out that many users may not have access to or the inclination to use specialized hardware like YubiKeys. The incident underscores the ongoing challenge of balancing user accessibility with the security of personal metadata in large-scale community platforms.