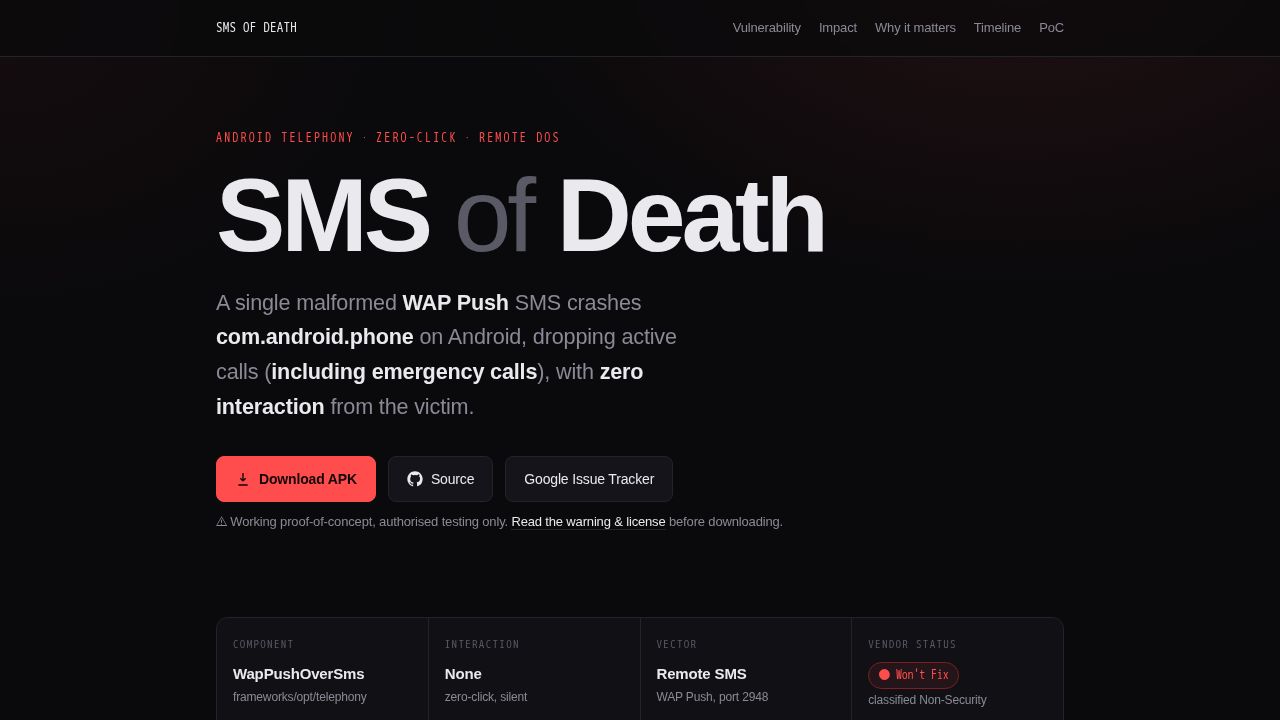
A security researcher, Mark Blaszczyk, has published a report detailing a vulnerability that enables a remote, zero-click Denial of Service (DoS) attack on Android devices. According to the report, the attack utilizes a WAP push—a method for sending data to a mobile device—to trigger a system-level failure. The researcher characterizes the exploit as 'silent' because it requires no interaction from the victim; the message does not appear in the standard messaging app, and the attacker's number is never displayed. The primary mechanism involves sending a specific payload to a target's phone number, which the researcher claims can cause the device to become unresponsive or crash.
While the researcher has provided technical details and even an APK for demonstration, the manufacturer has reportedly assigned a 'won't fix' status to the issue. This has led to significant debate within the security community regarding the severity of the flaw. Some observers questioned how a manufacturer could justify a 'won't fix' designation for a remote, zero-click vulnerability. Others pointed out the practical hurdles of such an attack, specifically whether mobile network carriers would accept or forward the specific WAP push payloads required to reach the device. The discussion also touched on the distinction between standard SMS text messages and specialized protocols like WAP push, which are handled differently by network infrastructure.
The disclosure has also raised questions about the current state of vulnerability reporting and the use of automated tools in the research process. Some commenters criticized the presentation of the findings, noting that the use of AI-generated summaries can sometimes obscure the technical nuances of a discovery. Despite these criticisms, the report serves as a case study in 'won't fix' vulnerabilities—instances where a flaw is acknowledged but left unpatched. This often occurs when the technical requirements for a successful exploit are deemed too high for widespread use, or when the risk is perceived as manageable by existing network-level defenses. The researcher suggests that publicizing the exploit may be a necessary step to pressure carriers or manufacturers into implementing broader blocks against such payloads.