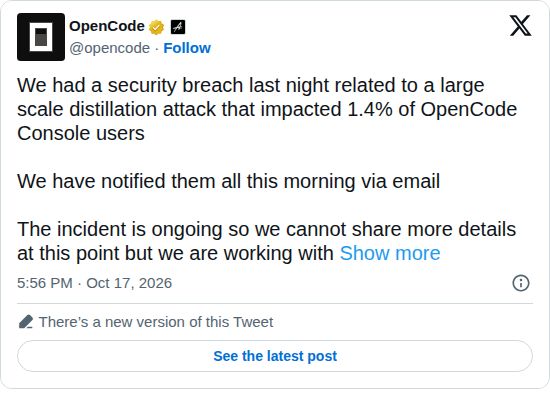
OpenCode has confirmed a security breach involving a large-scale distillation attack. The incident specifically impacted 1.4% of users of the "OpenCode Console," a hosted inference gateway and serving platform. While the company has begun notifying affected users via email, they stated that the incident is ongoing and provided limited specific details regarding the scope or technical mechanics of the breach.
Crucially, the breach is tied to the OpenCode Console rather than the OpenCode CLI or desktop applications. The Console functions as a managed platform—similar to OpenRouter—that allows users to connect their own AI platform accounts. This includes a "Bring Your Own Key" (BYOK) model where users provide their own API keys from providers such as OpenAI, Anthropic, or Google. Because these keys were stored on the Console's backend, the breach potentially exposed the credentials of those who opted to use the hosted service rather than running the software locally with their own credentials.
Discussion surrounding the incident highlighted concerns regarding the security of hosted API key management and the potential for unauthorized usage of those keys. Some users noted that the distinction between the various OpenCode products (CLI, Desktop, and Console) was not clearly communicated in the initial announcement, leading to confusion about who was actually at risk. While users who only utilize the local CLI or desktop versions with their own credentials are not affected, those who utilized the Console's hosted infrastructure face a race against time to invalidate their leaked keys. The incident underscores the trade-offs between the convenience of managed inference gateways and the risks associated with storing third-party credentials on a centralized server.