Software sandboxing is the practice of programmatically restricting a process's privileges without requiring administrative authority. While historically complex and often reliant on legacy techniques, modern sandboxing focuses on 'discretionary privilege dropping'—a design where developers explicitly limit what a process can do, complementing system-wide administrative policies rather than replacing them. A primary challenge in sandboxing is that traditional operating system interfaces, such as standard UNIX filesystem permissions, are often insufficient for modern application needs, like isolating third-party plugins within a web browser. Developers have historically turned to 'suid' binaries or kernel-level hacks to enforce restrictions, but these methods often increase the kernel attack surface or introduce security vulnerabilities. For instance, the misuse of Linux user namespaces for general sandboxing has led to significant security concerns, as it can inadvertently expose kernel code paths intended only for superusers. Instead of relying on such broad mechanisms, current best practices favor compartmentalization at the process level. By treating each component of an application as a separate process, developers can assign specific privileges to each compartment and manage communication through message passing. This approach aligns with the actor model, where processes act as independent entities that share no memory and communicate via defined interfaces, such as UNIX domain sockets. This model allows for the secure exchange of file descriptors, enabling fine-grained control over resources like files, pipes, and shared memory without granting the sandboxed process full system access. While platforms like FreeBSD offer specialized mechanisms like Capsicum for this purpose, and OpenBSD provides simplified tools like pledge(2) and unveil(2), the core principle remains the same: reducing the ambient authority of a process to the minimum necessary for its function.
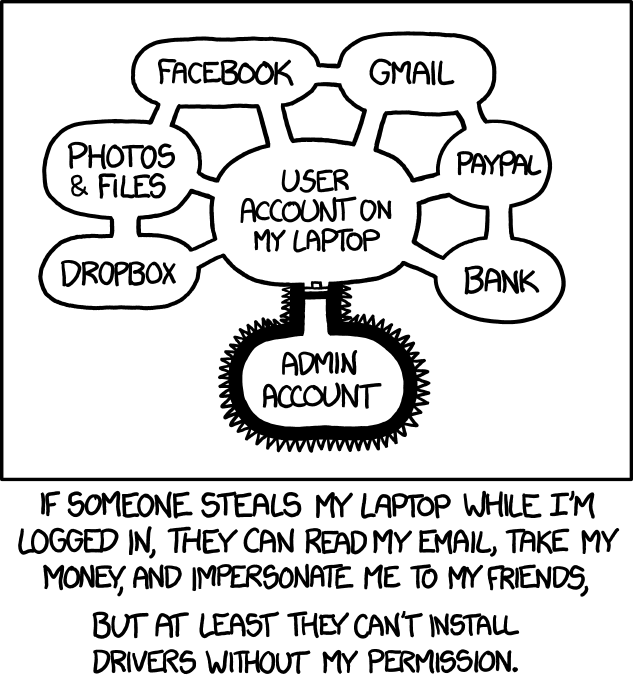
The article discusses how modern sandboxing aims to reduce the ambient authority of a process to the minimum necessary for its function, contrasting this with traditional system-wide permissions.
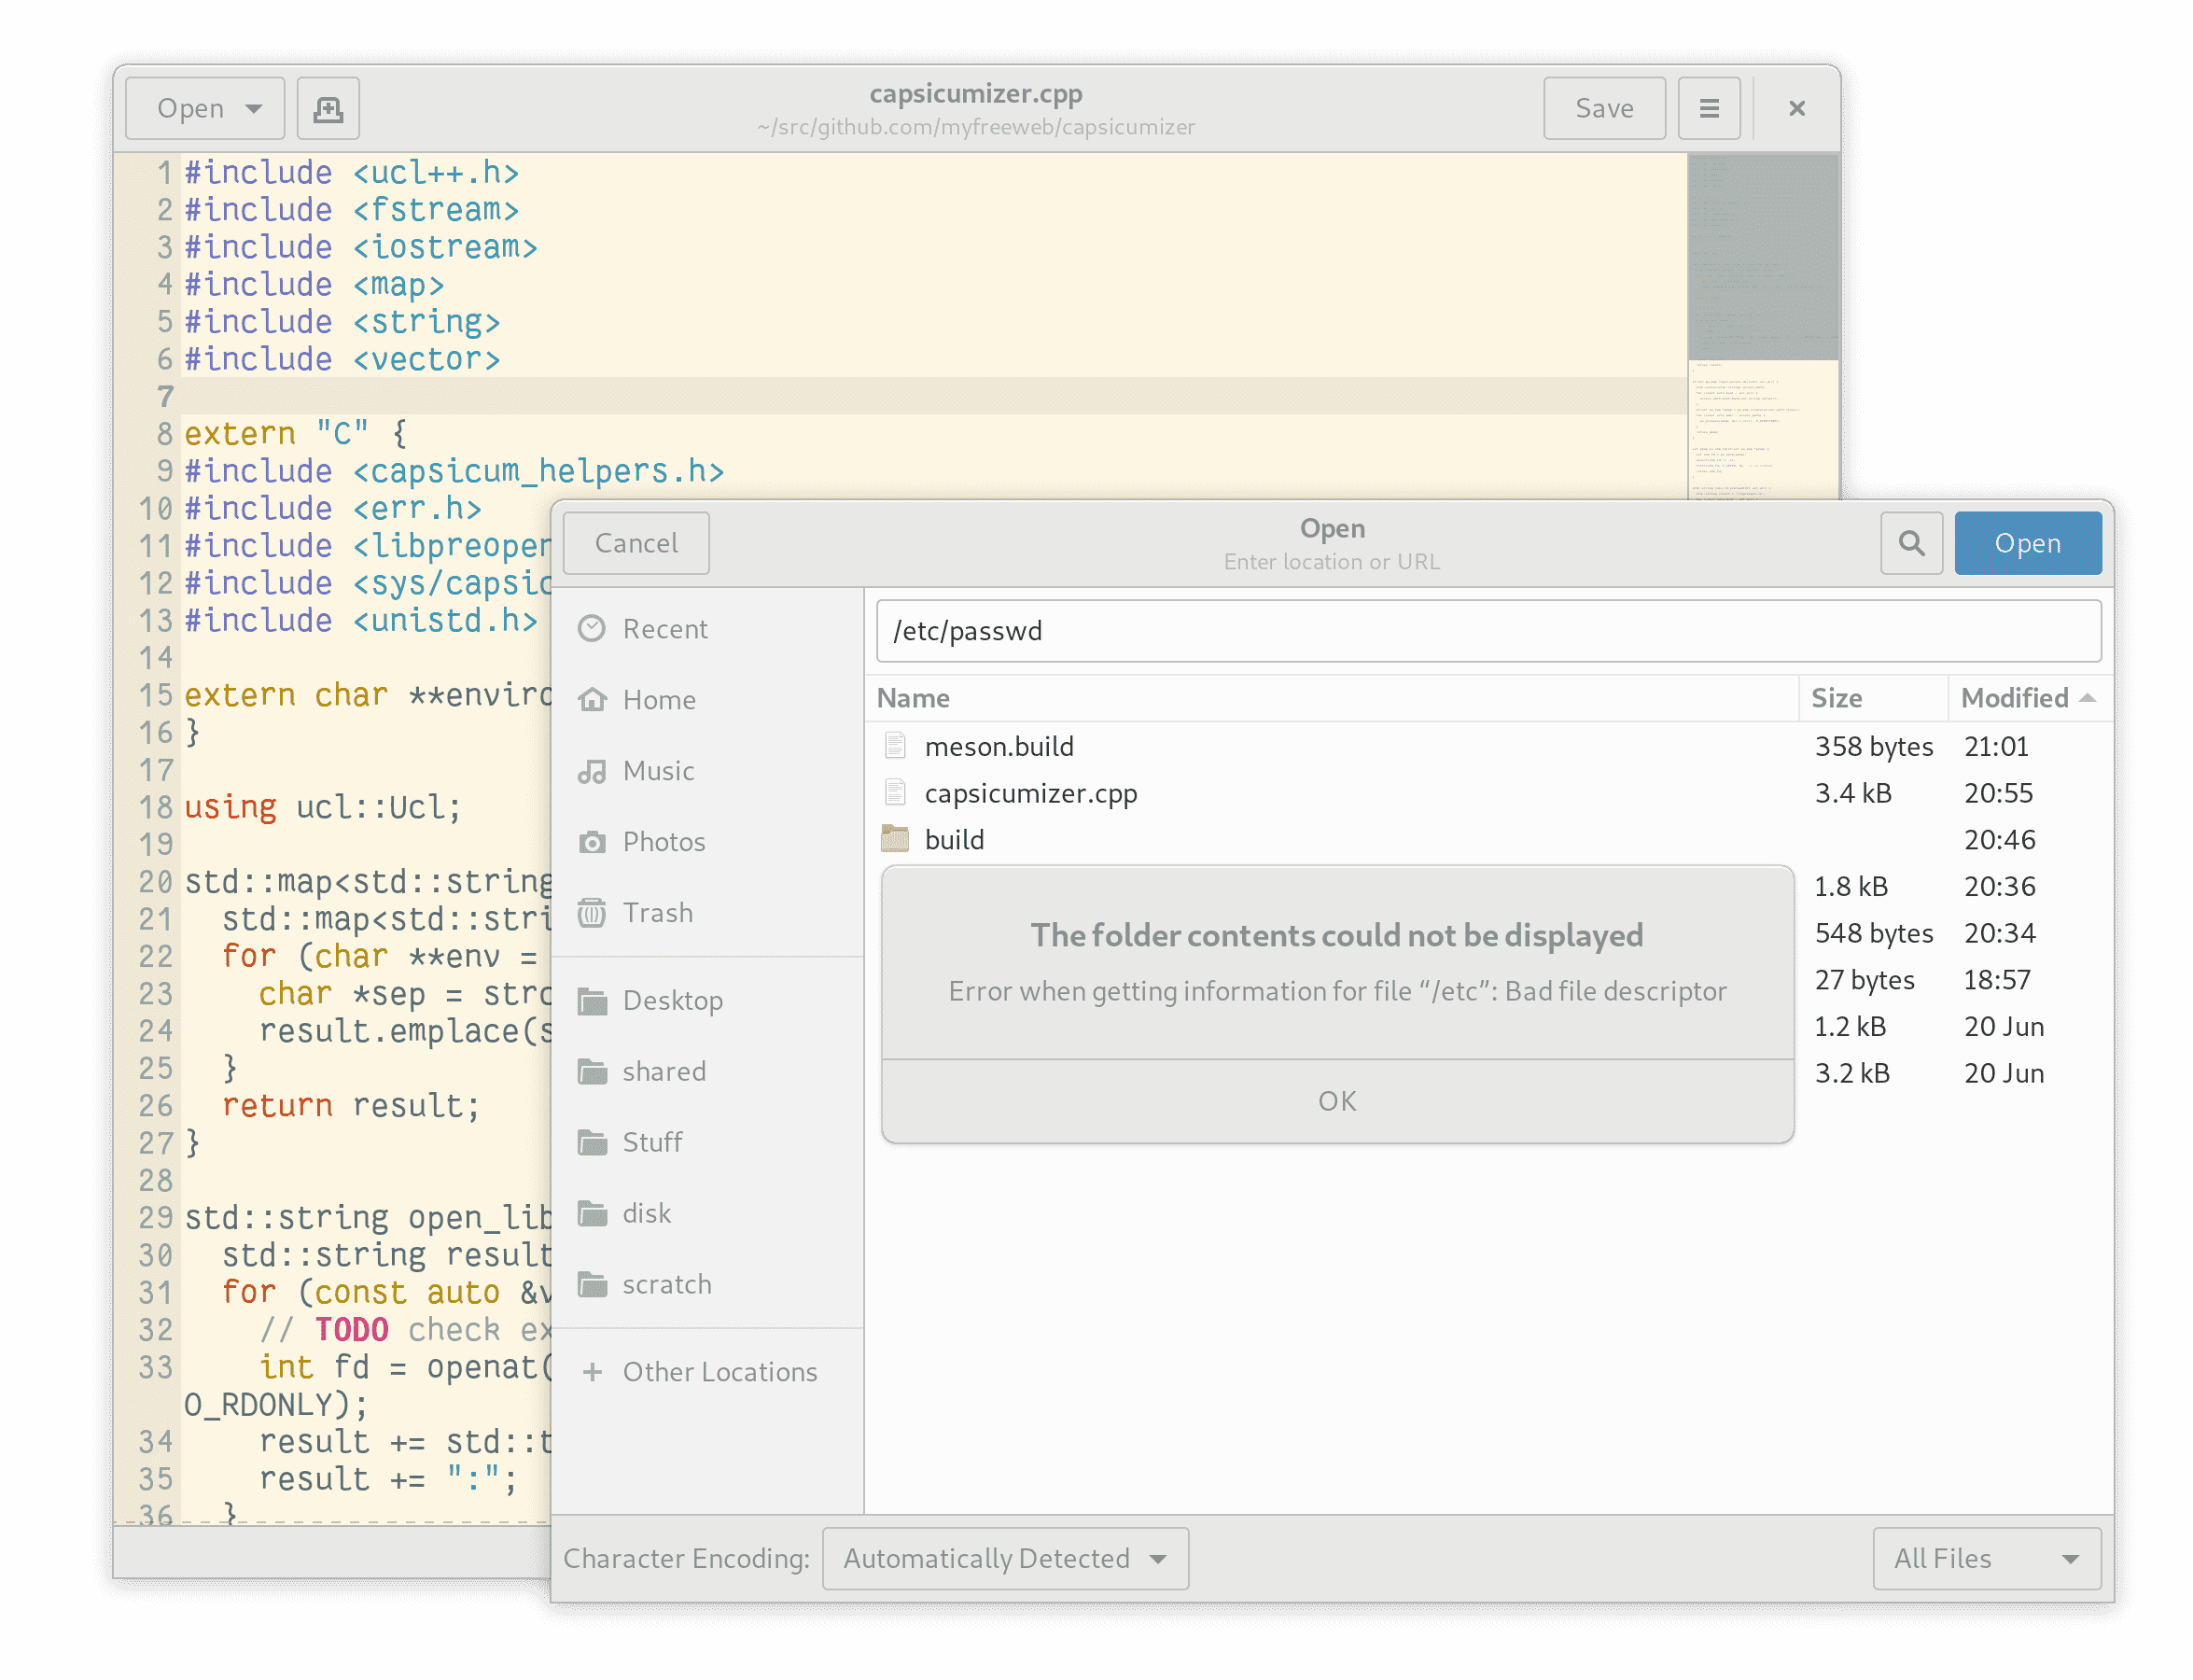
The text explains that traditional filesystem permissions are often insufficient for modern needs, such as isolating third-party plugins, and shows how compartmentalization can enforce stricter controls.